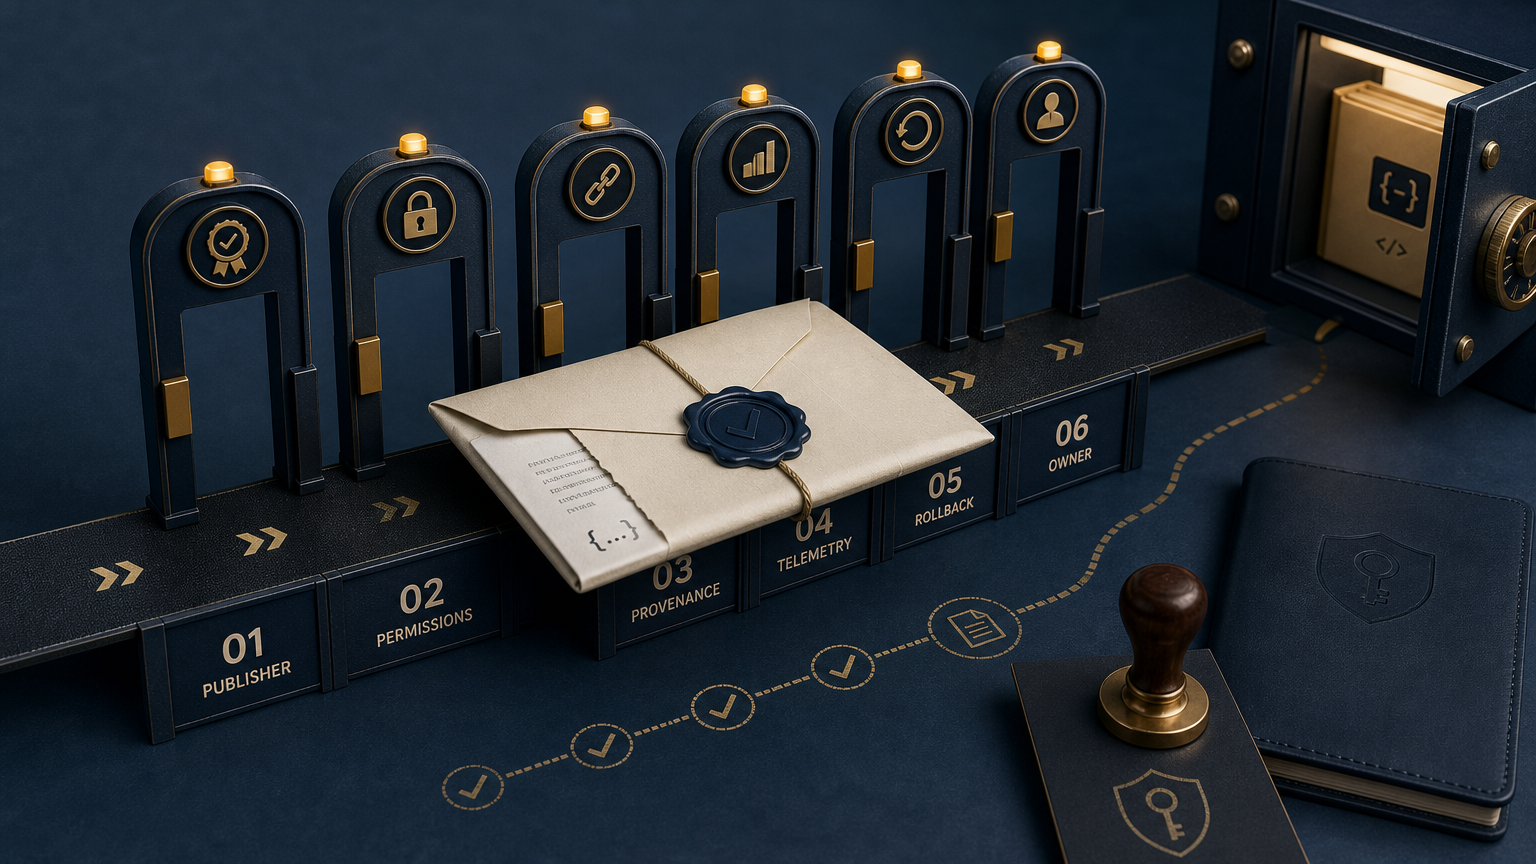
An AI extension may be a useful addition to a developer workflow, but it is still software introduced into an environment that can contain valuable code, data, tools, and identities.
The approval question is therefore larger than, “Does this feature work?” A more durable question is: What evidence supports granting this specific extension access for this specific purpose and environment?
This is not a claim that every extension presents the same level of risk. Editors, extension models, organizational controls, and deployment scopes vary. The point is to match the depth of review to the access being granted and the consequence of misuse, malfunction, or an unexpected change.
Start with scope and business purpose
A useful review begins by describing the proposed use in plain language. Identify who will use the extension, what problem it is intended to solve, which environment it will run in, and what information or systems could be in scope.
For example, an organization may choose to distinguish between:
- A limited evaluation using non-sensitive sample material.
- Use with internal source code.
- Use in environments containing privileged credentials or production-connected tooling.
- Use involving regulated, customer, or otherwise sensitive information.
These are adaptable scoping considerations, not universal deployment categories. Their value is in preventing a narrow pilot decision from silently becoming broad approval.
A decision record can also state what is out of scope. If an extension is approved only for a controlled test environment, that does not automatically authorize use with production repositories, privileged accounts, or sensitive data.
Review the publisher and the release in context
A recognizable product name or a marketplace listing can be useful signals, but neither should be the entire basis for a high-impact approval. Reviewers can seek evidence that connects the extension under consideration to an accountable publisher and a known release.
Relevant questions include:
- Who is responsible for publishing and maintaining the extension?
- Is there a credible security contact or escalation route?
- Can the organization identify the extension version it intends to permit?
- How are release changes communicated to customers?
- What controls, if any, help users distinguish expected releases from unexpected changes?
- What would prompt reassessment of a publisher, distribution channel, or release?
The evidence available will differ by vendor and marketplace. The goal is not to demand a single prescribed process; it is to make the approval basis explicit and proportionate to the planned access.
Examine access and data flows
Do not infer technical authority solely from an extension’s feature description. The relevant capabilities depend on the editor, its extension model, the operating system, local configuration, and the permissions of the user and environment in which it runs.
For the proposed deployment, ask what the extension is expected to read, write, execute, transmit, or retain. Areas worth considering may include:
- Workspace files and source code.
- Files outside the active workspace.
- Commands, processes, or development tools.
- Environment variables, tokens, or other locally available secrets.
- Network destinations and service integrations.
- Prompts, diagnostics, usage information, or other content sent outside the environment.
A practical test is proportionality: does each requested or available capability support the stated business purpose? If the answer is unclear, reduce the deployment scope, seek clearer evidence, or defer approval.
Ask how change will be managed
Approval is not a one-time event if software, dependencies, publisher ownership, permissions, or connected services can change over time. A review should define what changes require a fresh decision.
Possible reapproval triggers include:
- A material version or ownership change.
- Newly requested capabilities or broader access.
- New external services or network destinations.
- A significant change to data handling.
- A security event or material vendor notification.
- Expansion into a more sensitive environment.
The organization should also determine how it will identify the installed version and communicate an approved configuration to users. The objective is traceability: the approved deployment should be recognizable enough that a material change does not go unnoticed.
Make telemetry and outbound communication understandable
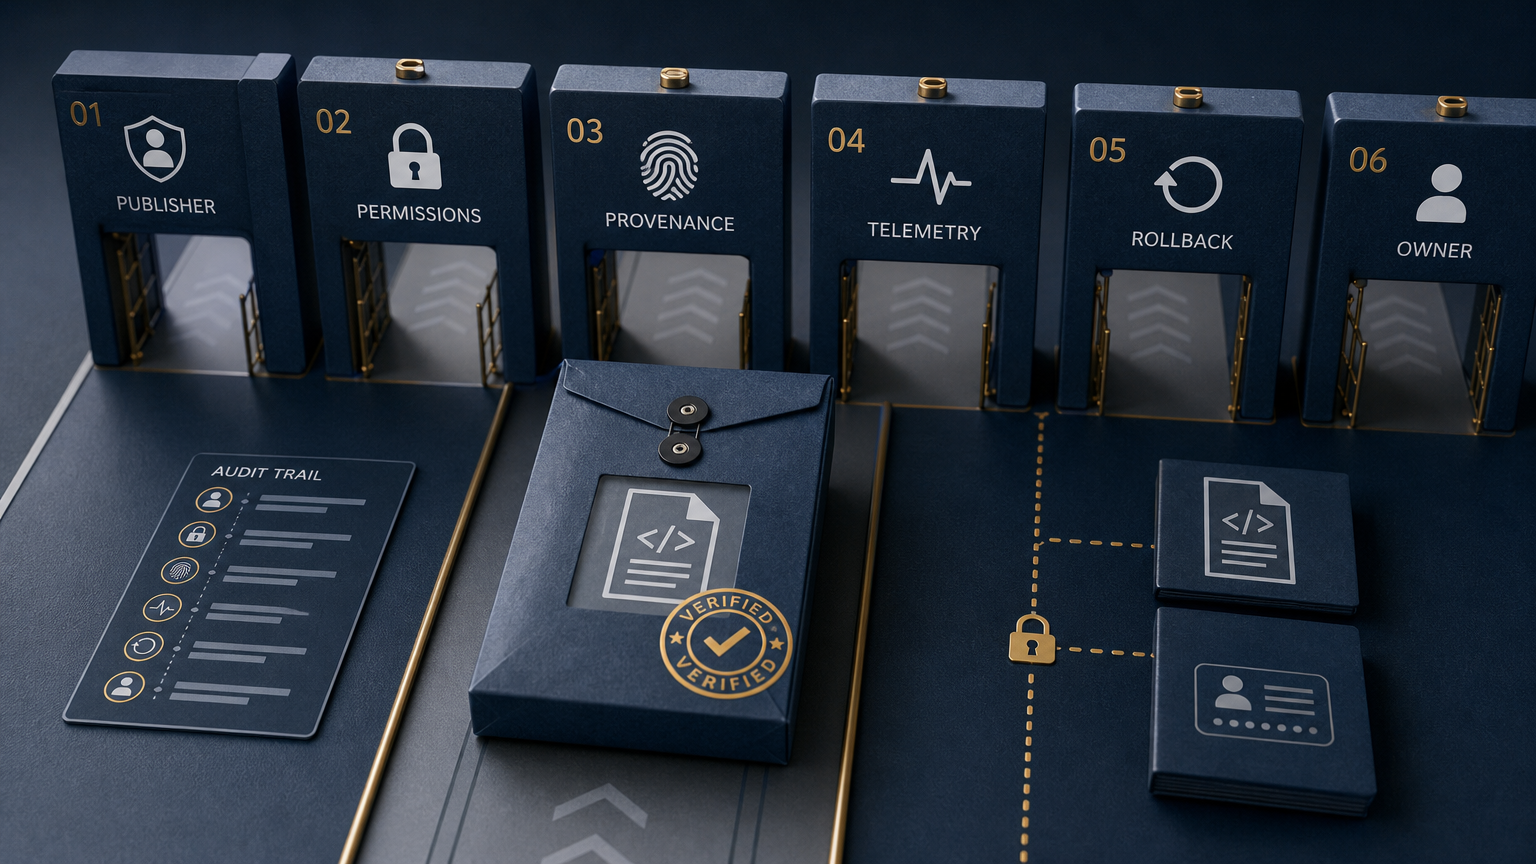
Data handling should be evaluated as an operational question, not only as a privacy-policy question. Teams need a practical understanding of what information may leave their environment, where it may go, and what they can observe or control.
Useful review questions include:
- What categories of content may be collected or transmitted?
- Which destinations and service providers are involved?
- What diagnostic or usage information is produced?
- What retention, access, and deletion terms apply?
- What administrative settings, logs, or network controls are available?
- Can the intended deployment limit use to an appropriate data boundary?
A vendor statement may be part of the evidence base, but an approval record should distinguish documented assurances from controls the organization can apply or observe in its own environment.
Prepare removal and response before broad access
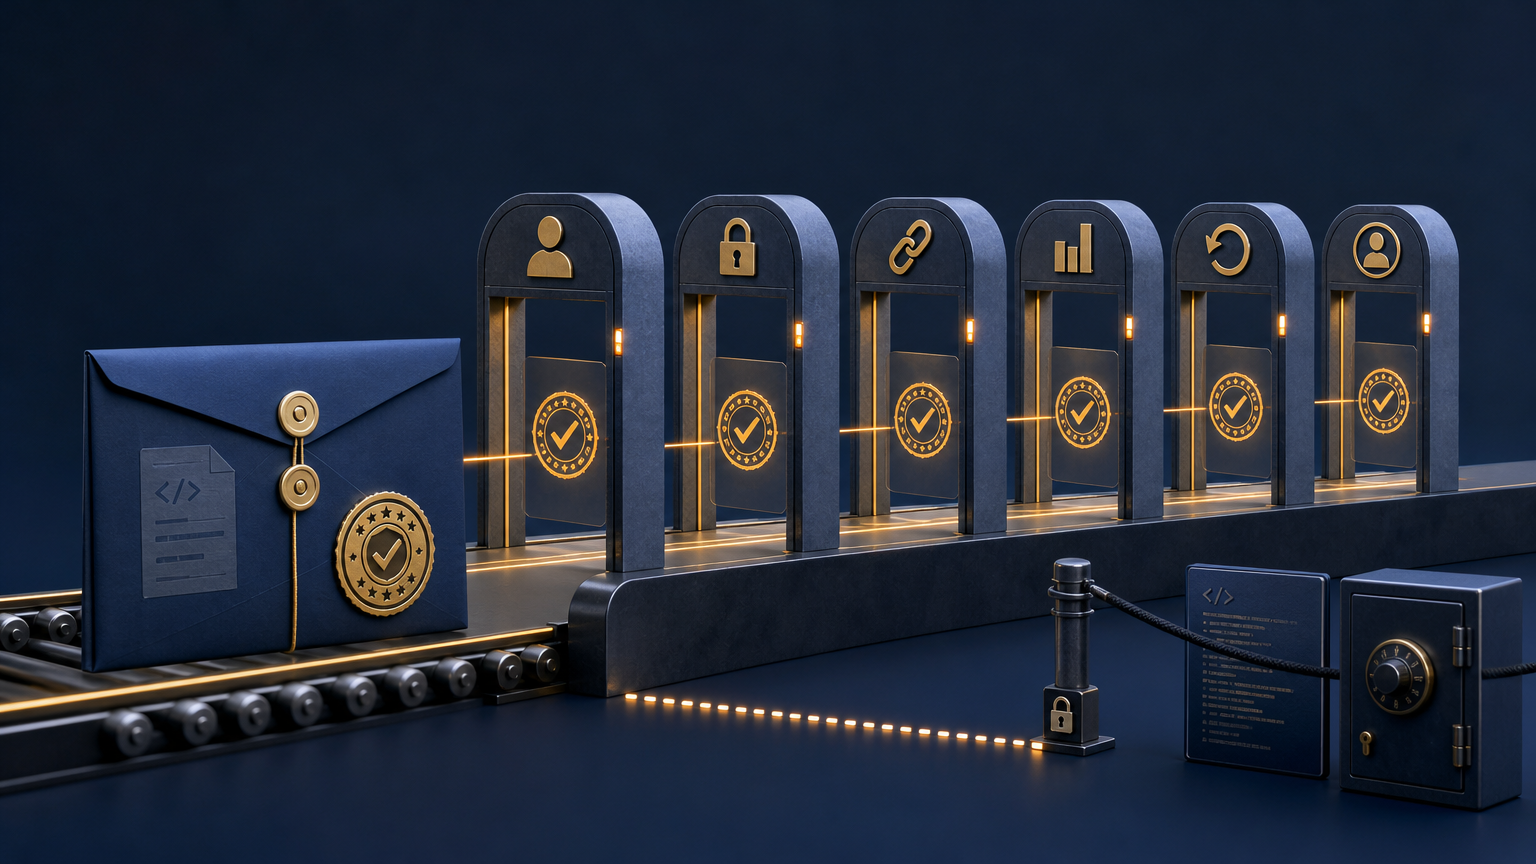
A responsible decision includes an exit path. Before expanding use, establish how the organization would disable or remove the extension, communicate a suspension, and restore an acceptable working state if trust changes.
The appropriate plan will vary, but it can address:
- How approved versions are recorded or controlled.
- How the extension can be disabled or removed from managed devices.
- Who can make a suspension decision.
- How relevant records or logs would be preserved under the organization’s processes.
- How potentially affected credentials, repositories, or integrations would be assessed.
- How developers would receive timely guidance and an alternative workflow.
Assigning an owner does not mean one person performs every technical or legal task. It means someone has the authority to coordinate the initial decision, involve the right teams, and prevent delay when an issue needs attention.
Use a decision record rather than a checkbox
A concise record can make assumptions, evidence, boundaries, and residual uncertainty visible. It also provides a starting point when a team later asks why a deployment was approved or whether a change requires review.
| Review area | Decision-record question | Example concern | |---|---|---| | Business purpose | What specific outcome and scope are proposed? | Use expands beyond the reviewed environment | | Publisher and release | Who is accountable for this version and path? | Release identity is unclear | | Access | What capabilities are relevant in this environment? | Available access is broader than the purpose | | Data handling | What may leave the environment and where? | Destinations or retention are not understood | | Change management | What triggers reassessment? | Material changes can occur without review | | Removal and response | Who can suspend use and coordinate next steps? | No timely, accountable response path |
The table is a framework, not a universal checklist. A low-impact evaluation may require less evidence than a deployment involving sensitive code or privileged systems. What matters is that the review reflects the real access and consequences of the decision.
Define conditions that pause or limit approval
Explicit stop conditions are often more useful than vague confidence statements. Depending on the environment and risk tolerance, an organization may choose to pause, narrow, or decline a deployment when:
- The accountable publisher or release cannot be established with sufficient confidence.
- The expected access is not proportionate to the stated purpose.
- Important data flows or external destinations remain unclear.
- The organization cannot identify the deployment it is approving.
- A material change has occurred without a reassessment.
- There is no workable suspension, removal, or escalation path.
These conditions do not require certainty that a problem exists. They recognize that high-impact access should not be granted when the organization cannot explain the boundary or respond effectively if that boundary changes.
A proportionate next step
For a proposed AI extension, bring together the people responsible for security, developer platforms, procurement, and the business use case. Define the smallest practical scope, document the evidence available, decide what would block expansion, and name the person accountable for coordinating a response.
The strongest approval is not a declaration that an extension is permanently safe. It is a bounded, evidence-based decision that can be revisited as the software, environment, and business use change.