Start with the governance question
Most model reviews compare a proposed version with a prior version. They assume that an accountable team or controlled process makes the change.
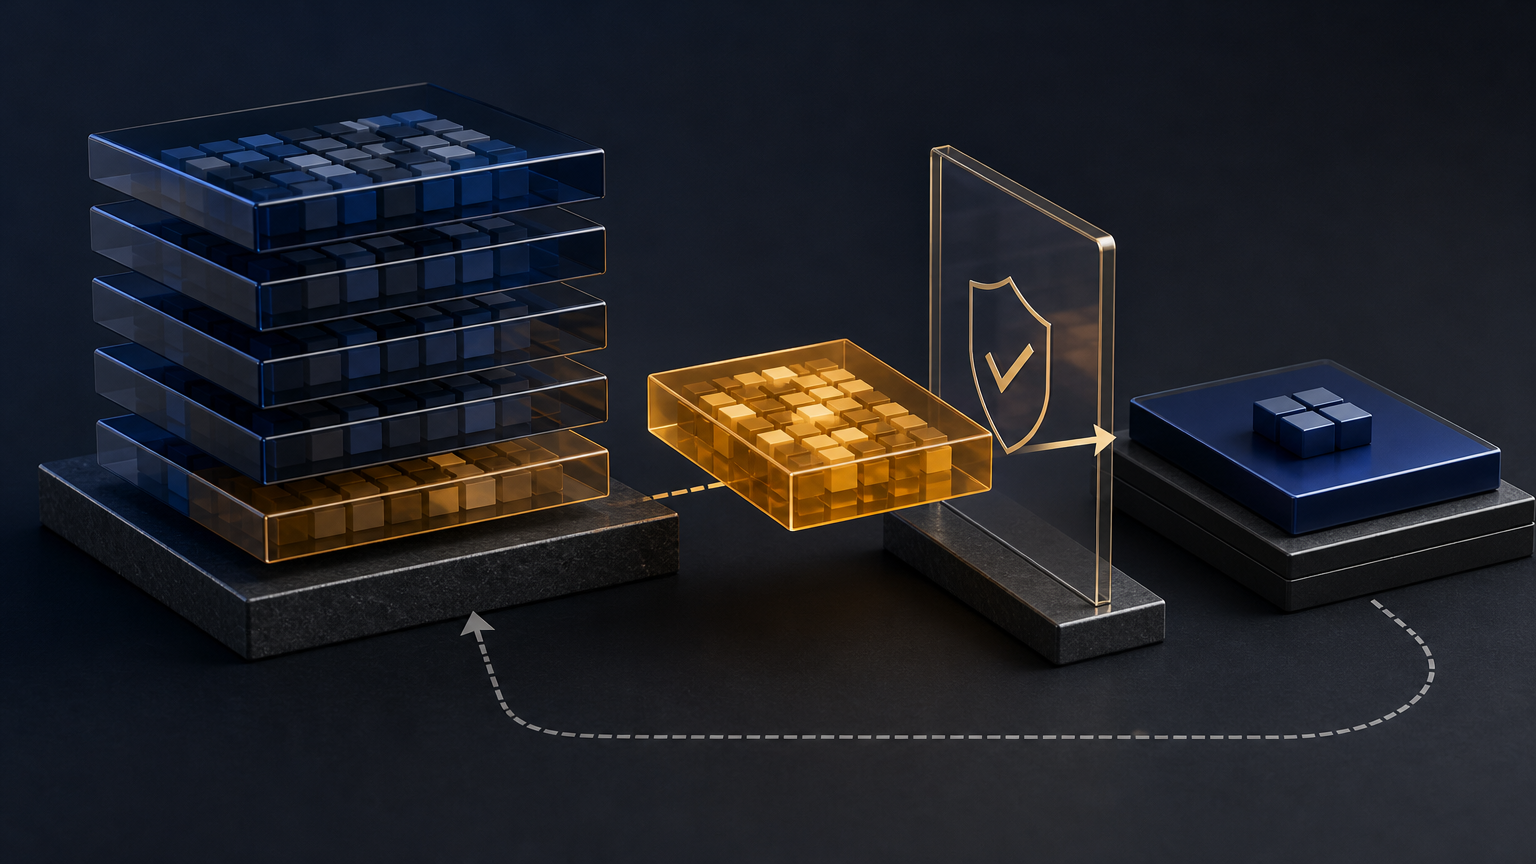
A self-modifying AI system changes the review problem. If a system can alter the model state that influences later outputs, operators need to understand more than whether a result appears improved. They need to know what changed, what evidence supported the change, who accepted it, where it may operate, and how it can be stopped.
The useful question is not simply, “Did the model get better?” It is:
Can the organization identify, assess, authorize, and reverse a change before that change affects a consequential workflow?
This is a governance framework, not a claim that every system described as self-modifying has the same capabilities or risks. The appropriate controls depend on the use case, the system’s permissions, the data involved, and the consequences of error.
Separate capability from deployment approval
A technical demonstration, benchmark result, or internal trial may show that a system can produce a changed model state. That does not by itself establish that the changed system is suitable for a live workflow.
Deployment approval requires a broader decision. An operator may need to consider:
- whether the claimed result can be reproduced under a documented evaluation process;
- whether relevant reliability, privacy, security, and authorization behaviors were assessed;
- whether the organization can identify the state that produced a particular output;
- whether promotion into the workflow is controlled by an authorized party; and
- whether the organization can suspend or restore the system when a problem emerges.
This distinction matters because task performance is only one property of a deployed system. A change that improves one measure may still be unsuitable if it creates regressions in behaviors that matter to the workflow.
A cautious starting point is to treat a model-state change as a material change when it could affect decisions, access, records, spending, sensitive information, or customer-facing outputs.
Build evidence around the change process
Evaluation should address the mechanism and governance of change, not only a before-and-after score. The following areas offer adaptable considerations for an evidence package.
Reproducible evaluation
Use defined evaluation procedures that are separated from the system’s own selection or approval process. Record the model state, test inputs, scoring approach, evaluator version, and operating environment used for each assessment.
Useful evidence is more than a single favorable result. It may include repeated runs, examination of failures, comparison against a prior state, and tests designed to reveal relevant regressions.
Behavioral assessment
Assess properties that matter to the intended workflow. Depending on the use case, these could include output consistency, handling of sensitive information, security boundaries, escalation behavior, factual reliability, and compliance with permitted actions.
The purpose is not to claim universal coverage. It is to make explicit which behaviors were assessed, which were not, and what boundaries follow from that evidence.
Change records
Maintain a durable record for each proposed and accepted change. A useful record can identify the prior and resulting states, the stated purpose of the change, evaluation evidence, applicable approvals, and acceptance time.
This record supports investigation after an incident and helps prevent uncertainty about which state was active when an output was produced.
Keep authority separate from proposal
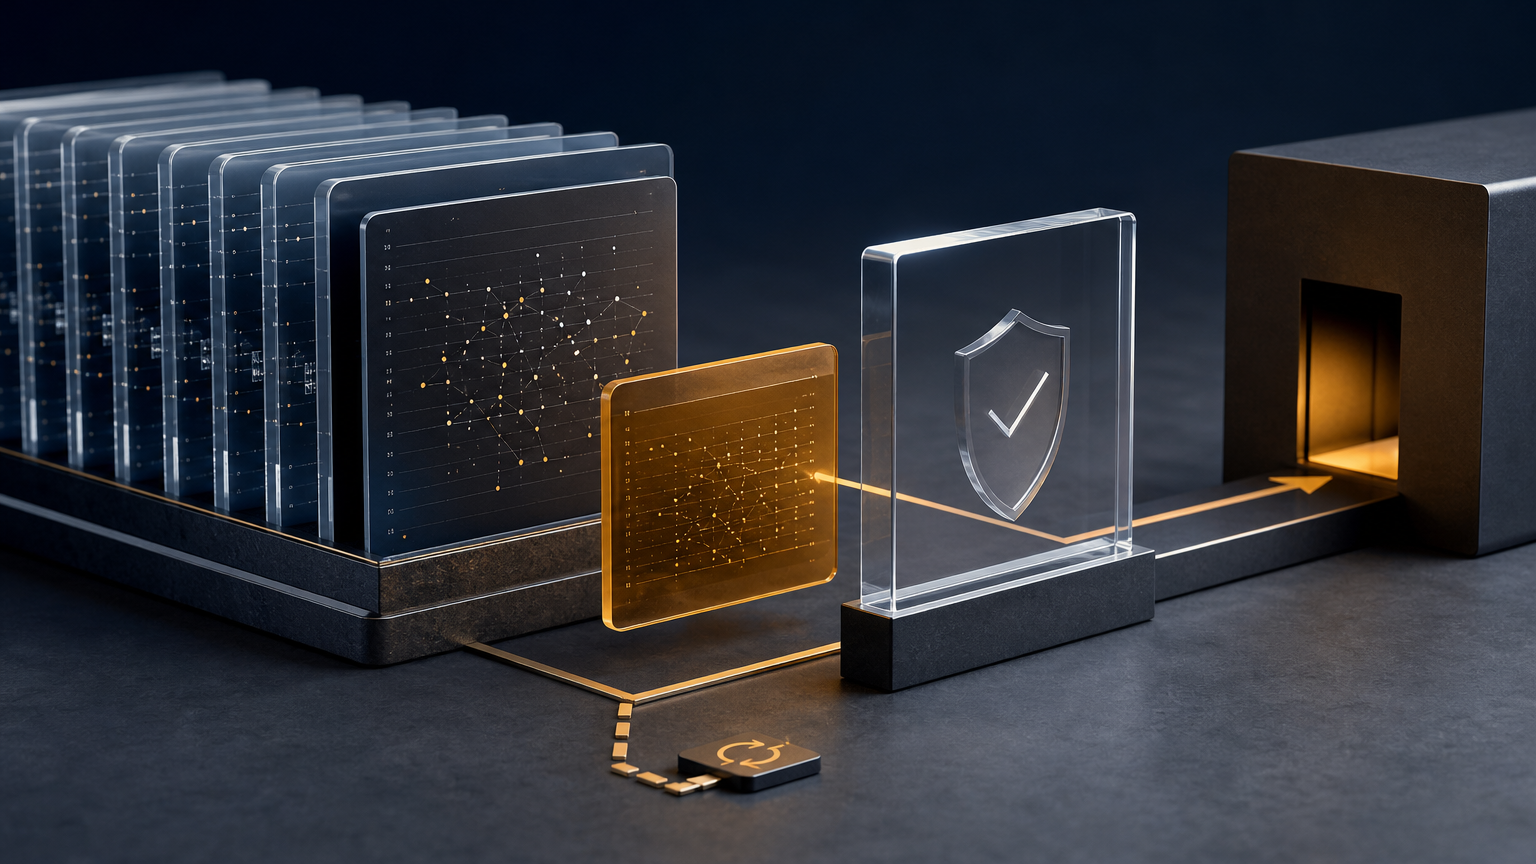
A system that proposes or tests a change should not be the sole authority that promotes the change into a consequential workflow. Separating these roles reduces the chance that the same mechanism both makes a change and declares it acceptable.
An adaptable approval design can distinguish among:
- Proposal: a candidate change is generated or identified.
- Evaluation: defined tests and reviews are performed.
- Authorization: an accountable human or independently governed process decides whether the change may be used.
- Promotion: the approved state is released only to the permitted environment.
The level of review should reflect the potential impact. A low-consequence experiment may use a simpler gate than a system that can affect financial decisions, sensitive data, regulated activity, or customer records.
Organizations should also define who may pause a system, reject a proposed change, and decide whether a previous state is the appropriate state to restore. Ambiguous authority is a practical risk during an incident.
Bound permissions and plan reversibility
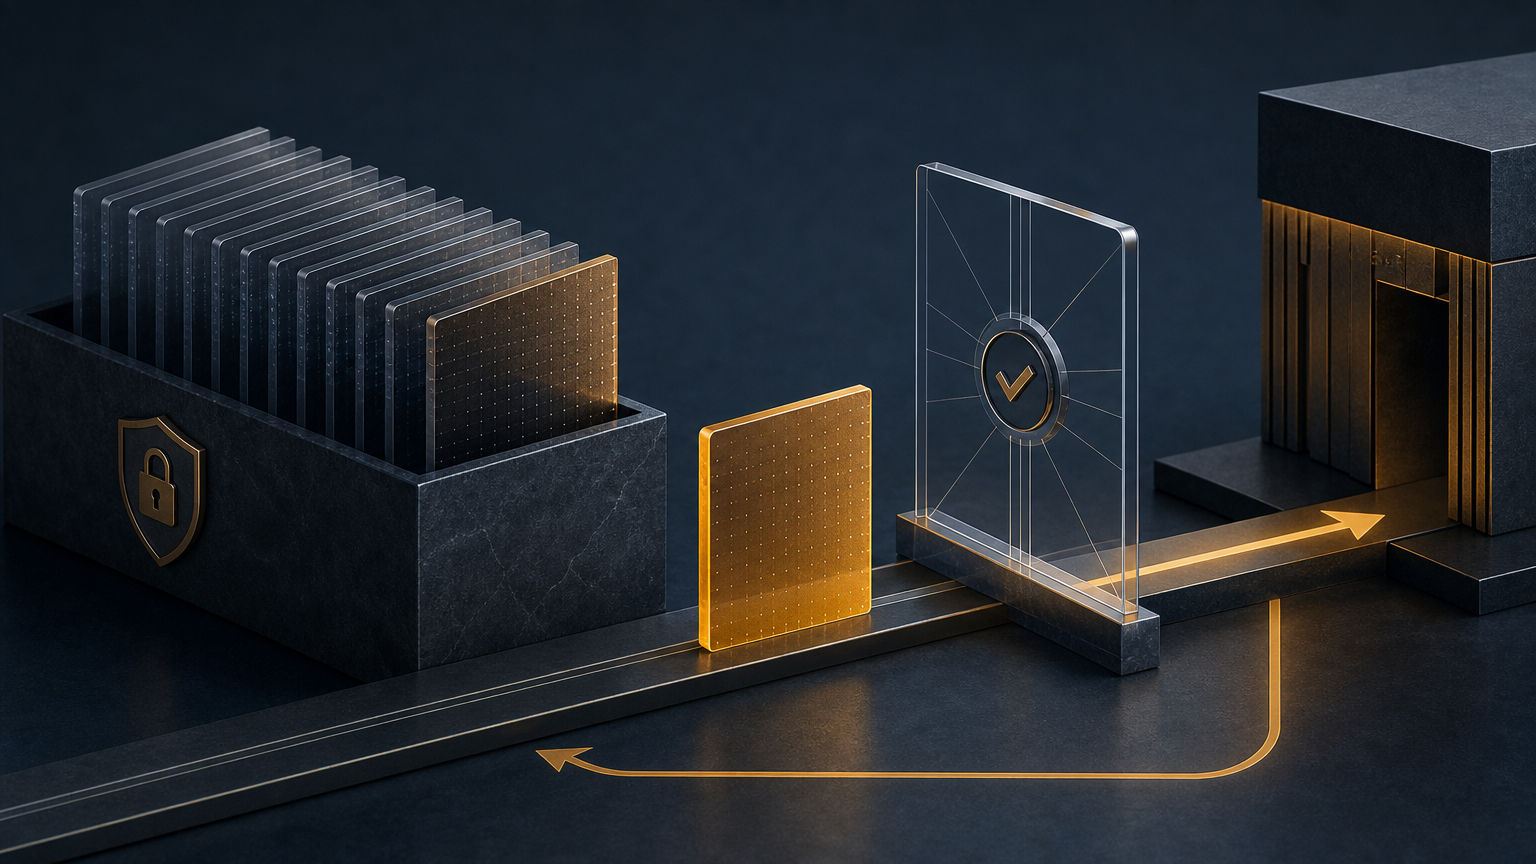
Permissions should match the narrow purpose of the use case. In early evaluation, organizations may choose to limit data access, downstream actions, and the environments in which changed states can operate.
A useful distinction is between permission to propose or test a change and permission to use that change in a business workflow. The latter should not follow automatically from the former.
Reversibility also needs operational definition. Before relying on a changed system, operators can establish:
- the trusted state or states available for restoration;
- the person or process authorized to suspend activity;
- the steps for restoring a known state;
- the records needed to determine when a disputed state was active; and
- the handling of work completed during the affected period.
A rollback plan is stronger when it has been exercised in an environment appropriate to the workflow. The goal is not to promise that every issue can be undone perfectly; it is to reduce uncertainty about the organization’s response when a change has undesirable effects.
Use an approval gate appropriate to the workflow
Before a changed model state affects a live workflow, decision-makers can use a focused set of questions:
- Identity: Can we identify the relevant model state before and after the change?
- Evidence: Was the change assessed through a defined evaluation process?
- Coverage: Were the behaviors most relevant to this workflow considered?
- Authority: Is approval assigned to an accountable party outside the change-proposal mechanism?
- Boundaries: Are access and downstream actions limited to the use case?
- Reversibility: Can activity be paused and a trusted state restored?
- Monitoring: Is there a plan to observe behavior after release and respond to material deviations?
A negative answer does not automatically produce the same decision in every organization. It should, however, prompt a decision about whether to add evidence, narrow the use case, limit the environment, or decline promotion.
For uncertain systems, a sandbox or low-consequence setting may provide a more appropriate place to learn than a workflow where errors can silently alter records, expose sensitive information, commit resources, or bypass established review.
Conclusion: govern the change, not just the score
Self-modifying AI raises a straightforward governance principle: when a system can alter the mechanism behind later decisions, the organization should increase the clarity of its evidence, decision rights, boundaries, and recovery plans.
Better task results can be useful information. They are not a complete approval case. A responsible decision considers the changed system, the process that produced the change, the authority that accepted it, and the organization’s ability to detect and respond if the change performs poorly in practice.
The practical next step is to create an evidence register for one narrowly defined use case. Specify the allowed actions, required assessments, approval authority, state history, monitoring signals, and rollback owner. That creates a basis for deciding whether a proposed change belongs in an experiment, a restricted workflow, or nowhere near a consequential process.