The operating question is not only autonomy
An AI workflow can be useful without being fully autonomous. The more important operating question is what the workflow may do when it encounters uncertainty, an error, an unexpected request, or a task that grows beyond its intended scope.
A budget is one way to establish that boundary. It should not be understood only as a finance setting. In an operational context, a budget can define how much of a resource a workflow may consume and how much consequence it may create before it must stop or ask for a decision.
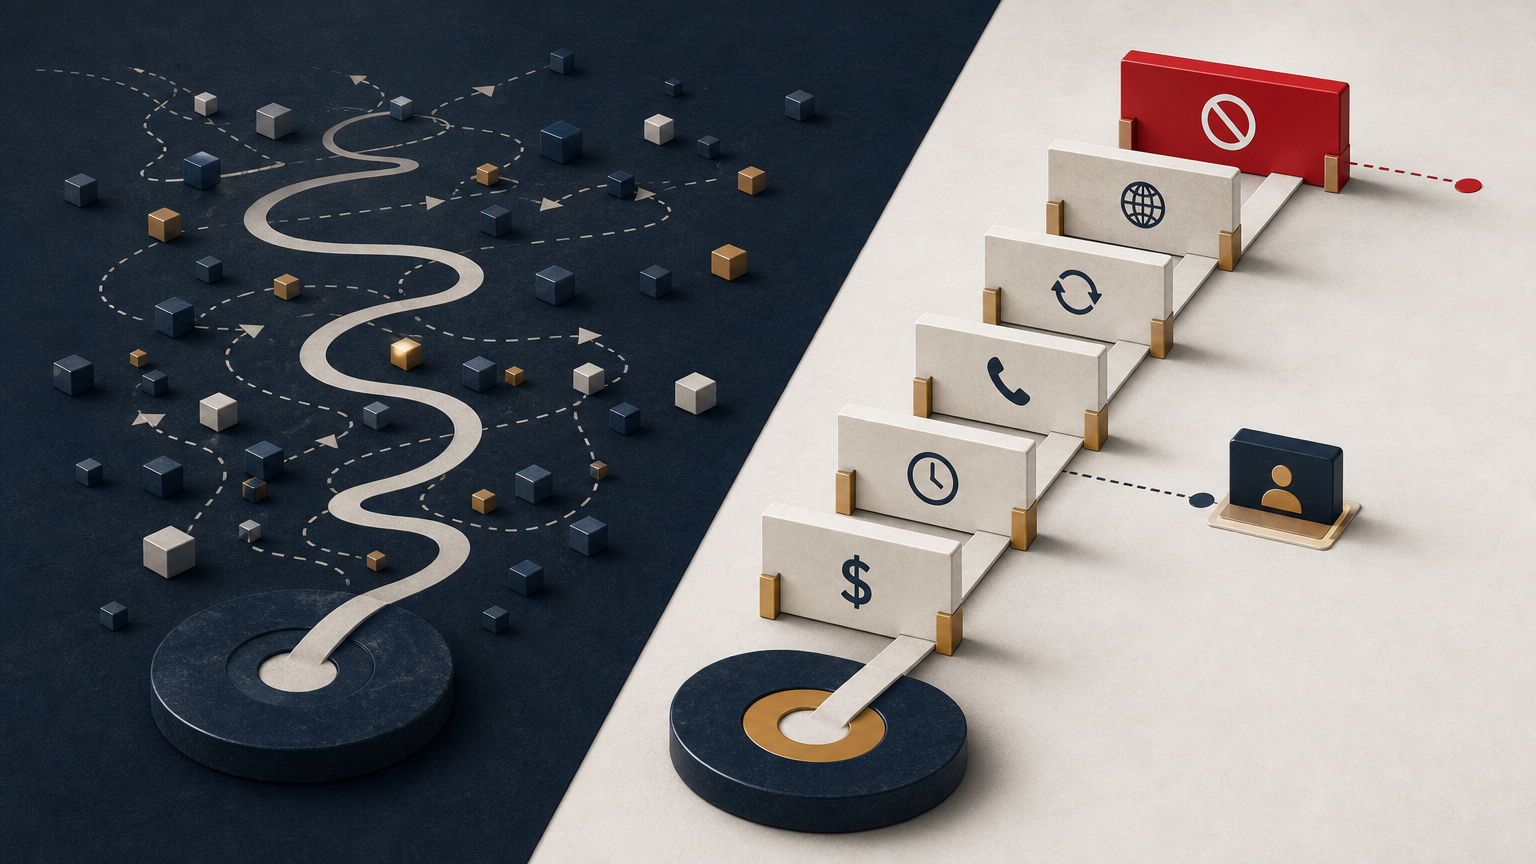
The goal is not to make every workflow rigid. It is to make authority explicit. A workflow should have a defined operating range rather than an assumed right to continue indefinitely.
A workflow budget has several dimensions
A dollar limit may be useful, but it is only one boundary. A workflow could remain within a financial limit while taking too long, making too many requests, or creating too many external changes.
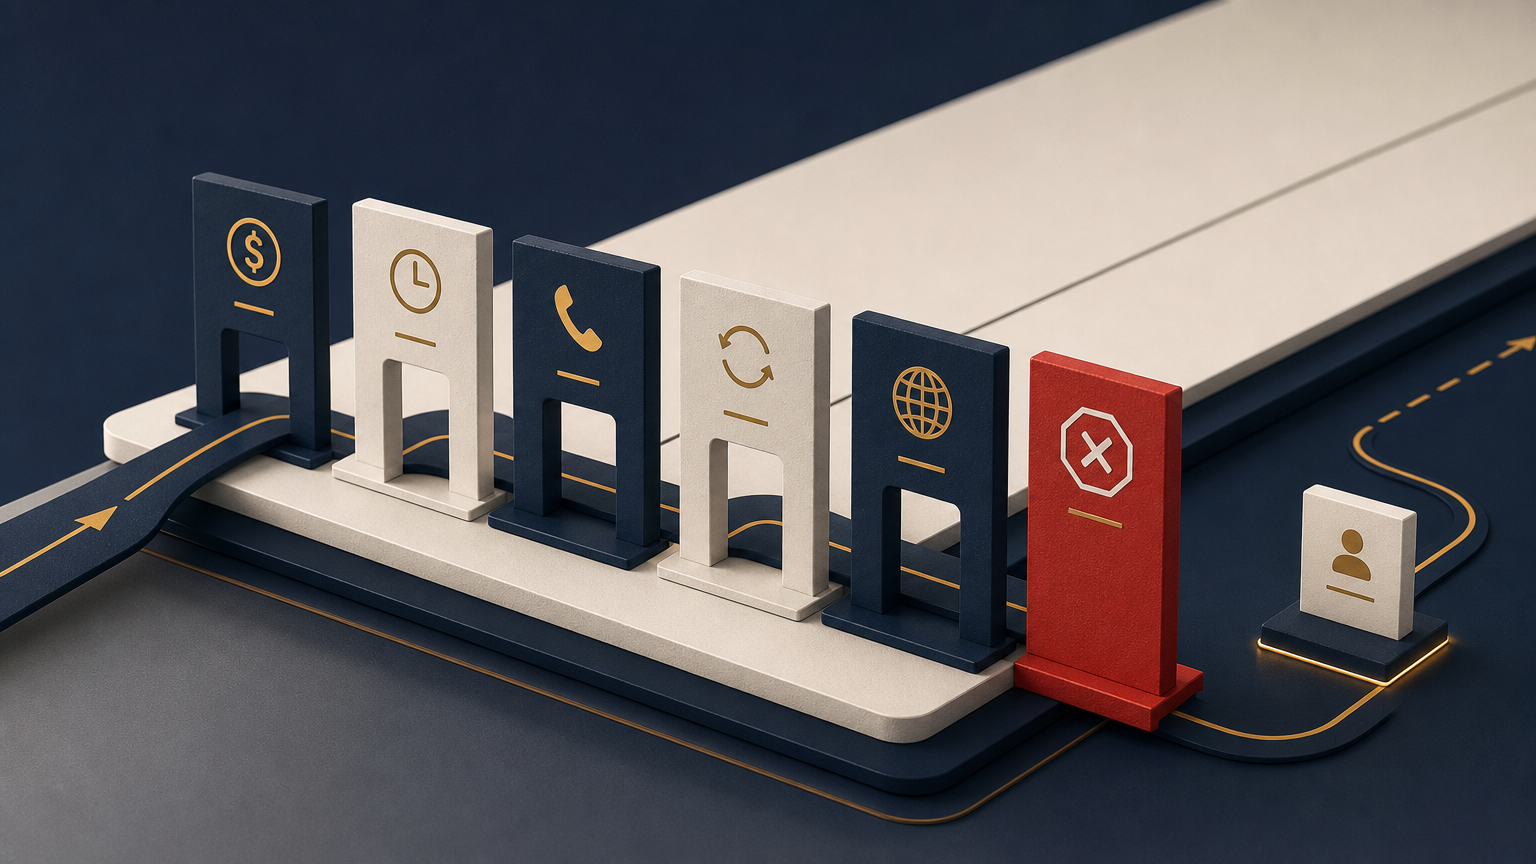
Consider defining separate boundaries for:
- Spend: The maximum approved cost associated with a run, task, or period.
- Tool calls: The number of permitted calls to retrieval, search, databases, messaging, or other connected systems.
- Runtime: The time a run may remain active before it stops or enters review.
- Retries: The number of attempts permitted after an error, timeout, or unsatisfactory result.
- Data access: The systems, records, or sensitivity levels available for the workflow’s stated purpose.
- Downstream actions: The type and number of external changes the workflow may make, such as drafting a message, updating a record, or creating a request.
These dimensions answer different questions. Spend asks how much the work may cost. Runtime asks how long it may continue. Action boundaries ask what the workflow may change. Data-access boundaries ask what information it may use. Treating them separately makes it easier to identify where the real risk lies.
Alerts and hard stops serve different purposes
An alert provides information to a person. A hard stop changes what the workflow is permitted to do next.
For this framework, a hard cap is an enforceable operating boundary: when the boundary is reached, the workflow does not continue with the affected activity unless an approved process allows it to do so. That is different from a notification that may be seen only after additional activity has occurred.
The distinction matters when no one is actively monitoring a run. A workflow that has reached its permitted call count, runtime, or action count should have a predictable outcome. Depending on the operating design, that may mean stopping, preserving its current state for review, or returning a status that identifies the decision required.
A stop can be inconvenient. Silent continuation can create a larger problem when the workflow is acting on incomplete context or repeating an unproductive pattern.
Set approval thresholds by consequence
Not every workflow action needs the same level of oversight. A low-consequence internal task may be appropriate for automatic completion, while a customer-facing, financial, sensitive, or difficult-to-reverse action may warrant a human decision.
One adaptable way to structure policy is to separate work into three bands:
- Within the automatic boundary: Actions consistent with the approved purpose, data scope, cost range, and action limit may proceed.
- Within a review boundary: Unusual, sensitive, more consequential, or less reversible actions pause for a named person to decide whether to continue.
- Outside the authority boundary: Actions beyond the workflow’s purpose, access scope, or stated limits do not proceed through an automatic exception.
The appropriate threshold is not determined by price alone. A low-cost communication sent to the wrong recipient may carry more consequence than a higher-cost internal analysis. Conversely, a resource-intensive internal task may be acceptable when its purpose and approval are already clear.
These are operating considerations rather than universal rules. The right policy depends on the organization, the workflow, the people affected, and the consequences of error.
Design a useful stop state
A workflow that stops at a boundary should still leave an operator with a usable outcome. A clear stop state can identify:
- which boundary was reached;
- what work was completed;
- what work remains incomplete;
- whether any external action occurred; and
- which person or role may decide what happens next.
This information helps prevent a stop condition from becoming a source of confusion. It also supports safer review of partial work.
When defining the process, operators can ask:
- Can the work resume without repeating an external action?
- Is a partial result suitable for use, or should it be reviewed first?
- Who owns the decision to approve an exception or restart?
- What record is needed to understand why the workflow stopped or continued?
A boundary is more likely to remain in place when the resulting review process is understandable and proportionate.
Spending boundaries are only one layer
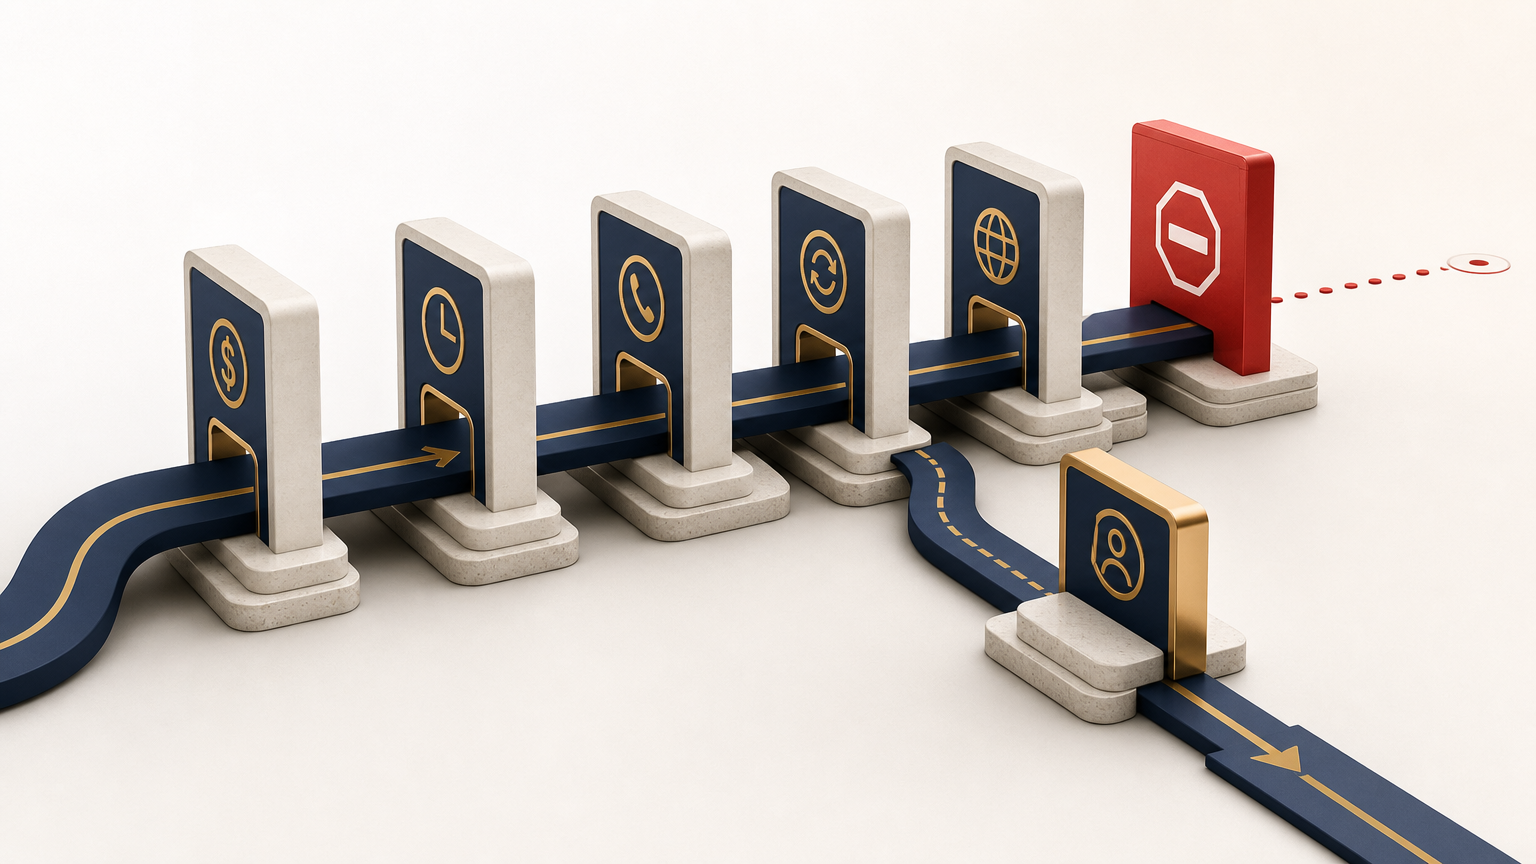
Cost controls can be valuable, but a spending boundary alone does not answer whether a workflow should contact a customer, modify a business record, access sensitive information, or repeat an external action.
Those questions belong to the workflow’s broader authority model. A practical model connects resource limits with purpose, permitted tools, data scope, approval requirements, and ownership.
This also avoids treating a financial boundary as a substitute for decision-making. A workflow might be inexpensive and still inappropriate for a particular action. It might also be costly but acceptable when the purpose, scope, and approval are explicit.
Questions to ask before expanding autonomy
Before giving a workflow more tools, broader data access, or authority to make external changes, review its existing boundaries:
- What is the maximum acceptable cost for one run, one task, and one operating period?
- Which connected tools can cause an external effect rather than only retrieve information?
- What is the maximum number of calls and retries before the workflow stops or enters review?
- Which actions require a named human approver?
- What should happen when a boundary is reached during partially completed work?
- Can the organization understand the workflow’s actions, approvals, and outcome afterward?
- Which exceptions are permitted, how long do they last, and who can authorize them?
If these questions do not have clear answers, additional autonomy may increase exposure faster than it increases usefulness.
The takeaway
AI workflows should operate inside explicit boundaries that match their purpose and potential consequences. Consider limits for spend, tool calls, runtime, retries, data access, and downstream actions. Pair those limits with approval thresholds for consequential work and a clear process for safe stopping.
Broader autonomy is easier to manage when it is earned through predictable operation inside defined boundaries, rather than assumed by default.