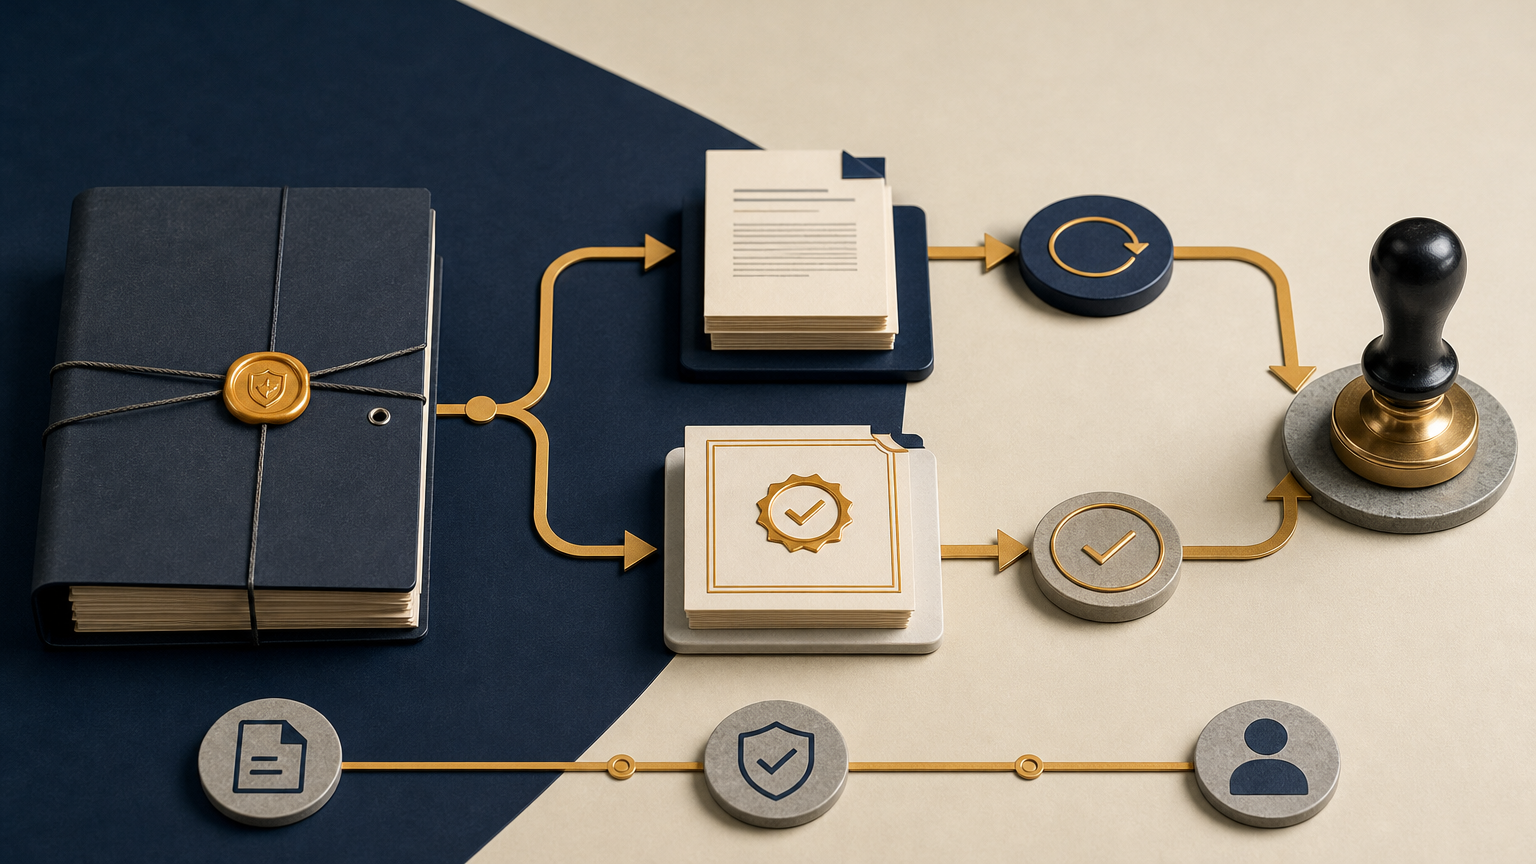
The operator’s problem is not whether the AI sounds convincing
An AI system may produce a detailed explanation of why a software change is safe. It may identify edge cases, propose a proof strategy, summarize test results, or describe a formal property.
None of those outputs, by themselves, settles whether a consequential release should proceed.
The more useful question is: what claim is being made, what evidence supports it, what assumptions limit it, and does that evidence apply to the change under review?
This distinction matters because assurance claims are bounded. A result may be useful and technically sound while still leaving important operational, security, or business risks outside its scope.
Treat verification claims as bounded evidence
The word “verified” can obscure more than it explains unless the underlying claim is stated precisely.
A review should distinguish between a model’s narrative, an automated analysis result, a formal claim, and a release decision. These are related, but they are not interchangeable.
For example, a statement such as “a defined failure condition was not found within a stated scope” is materially different from “the change is safe.” The first can be reviewed against its method and boundaries. The second is too broad to evaluate without additional context.
A useful evidence record describes:
- the property or condition assessed;
- the code, artifact, configuration, or version in scope;
- relevant inputs, environments, and assumptions;
- the method used to obtain the result;
- exclusions, unresolved questions, and residual risks; and
- the decision the evidence is intended to inform.
This approach does not diminish formal methods, testing, or AI-assisted analysis. It places each form of evidence in the decision it can credibly support.
Five questions to guide review
1. What exact property was assessed?
“Verified” is incomplete without a property.
Reviewers can ask whether the work concerns a specific safety condition, a security invariant, conformance to a stated rule, a class of failures, or another defined behavior. The answer should be understandable to both technical and accountable decision-makers.
A bounded statement is easier to govern than a broad assurance label. It also helps prevent a narrow result from being reused as evidence for unrelated claims.
2. Does the specification reflect the risk that matters?
Formal and automated methods evaluate a stated condition. They do not independently determine what the organization ought to require.
A specification may omit business rules, privacy expectations, prohibited outcomes, unusual inputs, recovery behavior, or human operational requirements. Reviewers should consider whether the chosen condition meaningfully addresses the risk behind the release decision.
3. How was the result checked?
A model-generated explanation can be useful context, but it is not the same thing as a result evaluated by a designated verification or testing mechanism.
For higher-consequence decisions, teams may choose to record the tool or checker used, the artifact it evaluated, the reported outcome, and any exclusions or unresolved obligations. Whether a checking mechanism is sufficiently trustworthy or independent depends on the organization’s risk model, trust boundaries, and review process.
4. Does the result apply to the proposed release?
Evidence is most useful when it is traceable to the item under review. Material changes in source code, build outputs, configuration, dependencies, runtime conditions, or packaging can alter the relevance of an earlier result.
Reviewers can ask what links the assessed artifact to the artifact proposed for deployment and whether important environmental assumptions still hold.
5. What remains outside the assessment?
A responsible review asks not only what passed, but also what was not established.
Potential gaps may include external-system interactions, access decisions, data handling, real-load behavior, operational procedures, supply-chain exposure, and conditions not represented in the assessment. Stating these limits plainly supports a more informed release decision.
An adaptable approval record for consequential changes
Not every software change warrants the same evidence package. Teams can make the level of review proportionate to the consequence of failure, the reversibility of the change, and the uncertainty involved.
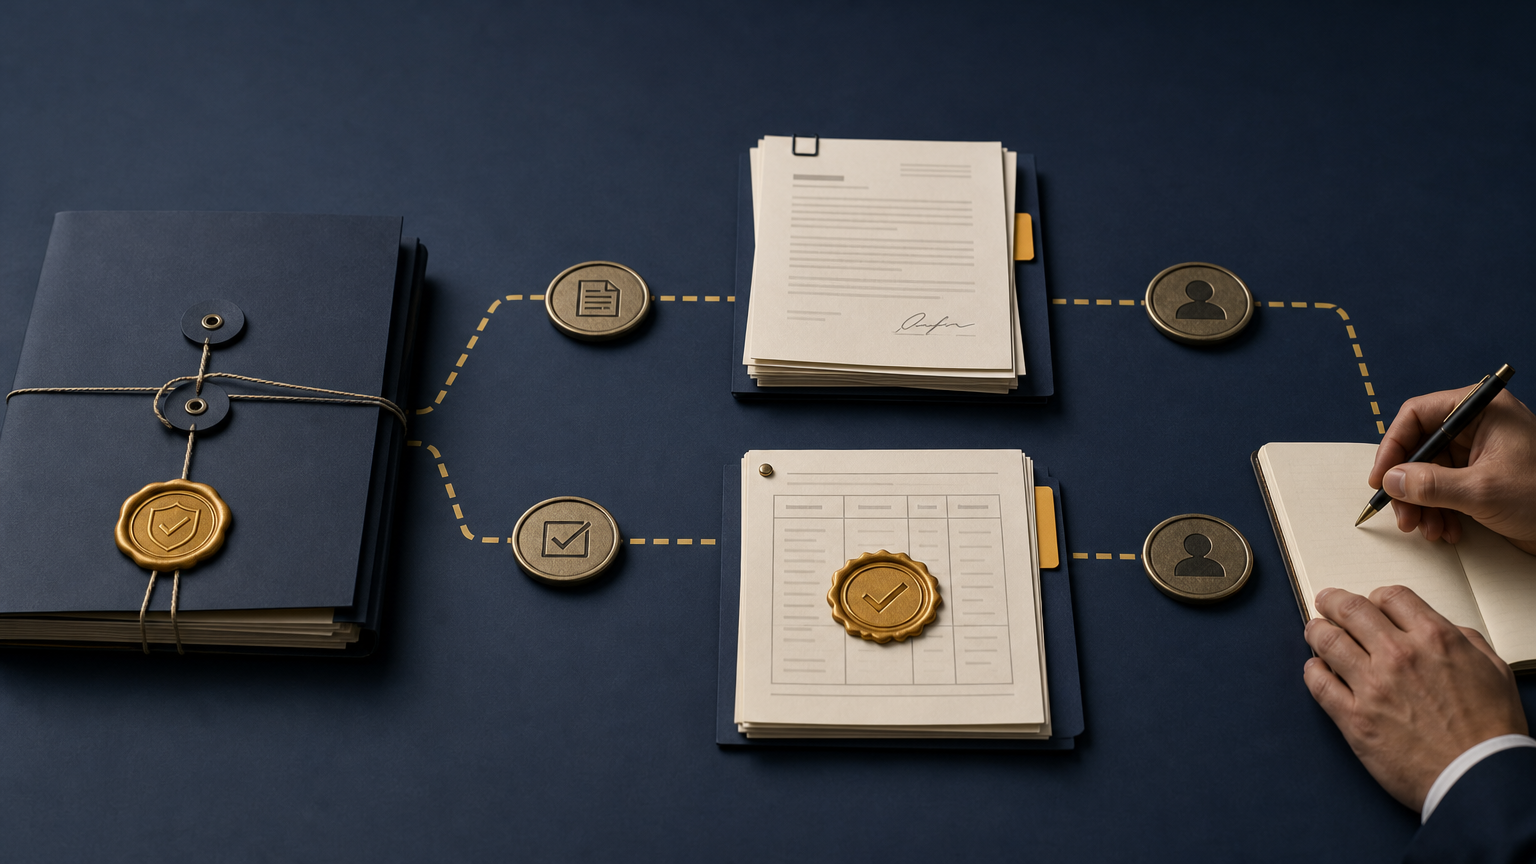
For a consequential release, an approval record might include:
- The claim: the property assessed and the risk it is intended to address.
- The scope: the relevant artifact, version, inputs, environment, and assumptions.
- The result: the output of the selected analysis, test, or verification process, including limitations.
- Traceability: the connection between the assessed item and the proposed release.
- Residual risk: important behaviors or scenarios that remain outside the assessment.
- Accountability: the people authorized to accept residual risk and approve the release.
- Containment: an appropriate rollback, disablement, staged-release, or monitoring approach.
These are adaptable considerations, not universal requirements. Their purpose is to make the release rationale reviewable rather than to create a generic “AI verified it” status.
Keep evidence generation separate from approval authority
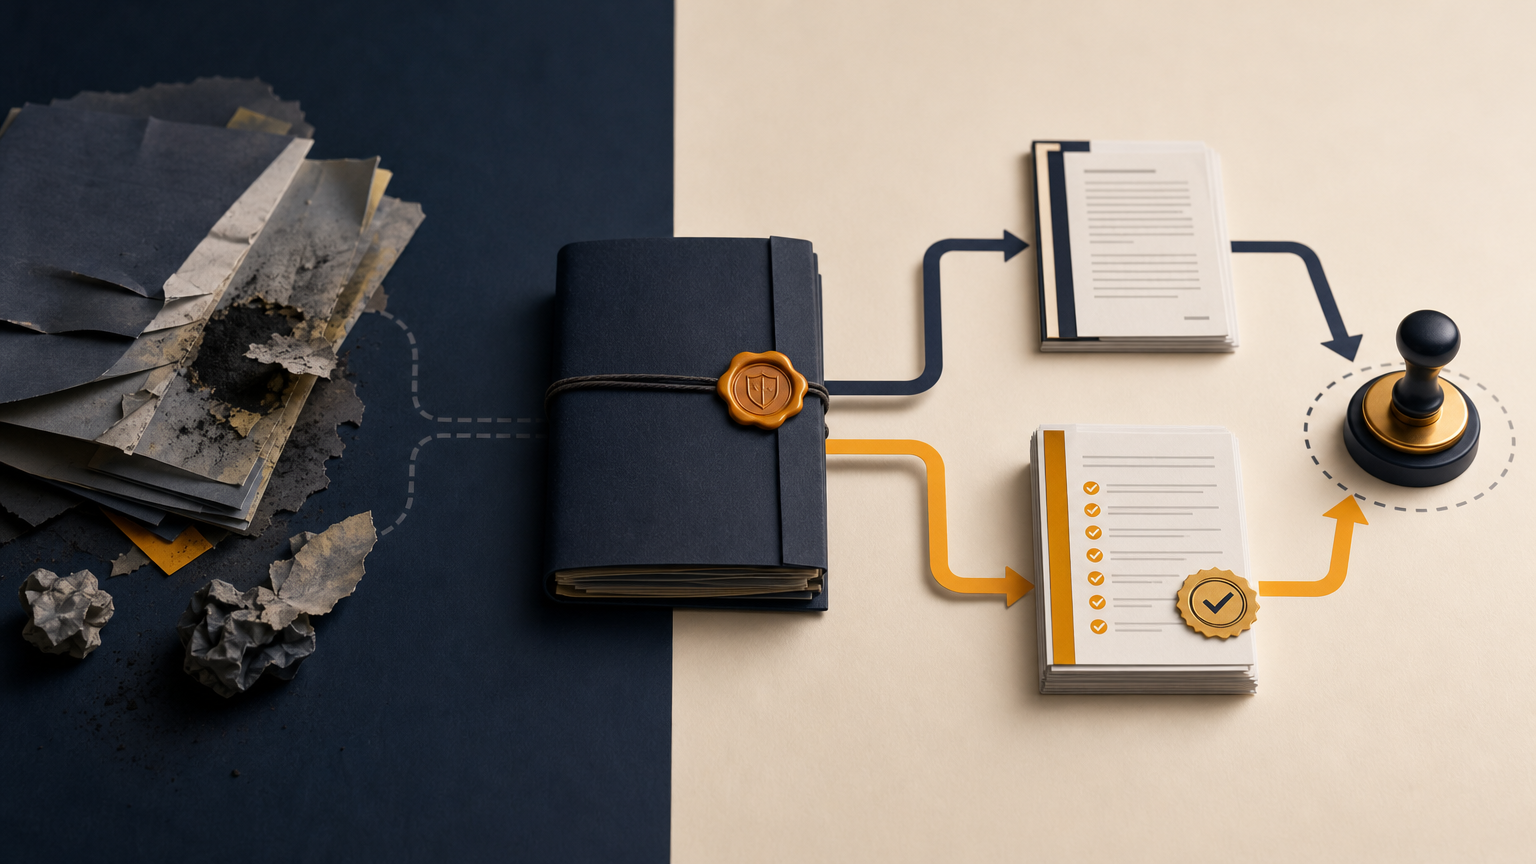
AI can help generate candidate explanations, identify questions, summarize evidence, and assist technical analysis. Approval authority is a separate responsibility.
A sound governance approach preserves that separation. It identifies who defines the required assurance claim, who evaluates whether the evidence is adequate for the decision, who accepts remaining risk, and who can pause or constrain a release.
This is especially important when AI output is persuasive. Fluent prose can make uncertainty appear resolved even when assumptions are incomplete or the scope is narrow. A structured record helps reviewers focus on the claim and evidence rather than confidence of presentation.
The takeaway
AI-assisted software verification can contribute valuable evidence, but it should be assessed as bounded evidence rather than as a universal approval signal.
Before approving a consequential change, review the property being assessed, its scope and assumptions, the basis for the result, its connection to the proposed release, and the risks left outside the assessment. Then make the release decision through the organization’s accountable governance process.
The practical standard is not whether an AI system sounds convincing. It is whether the available evidence is proportionate to the consequence of being wrong.